What if Identity Didn’t Exist?
The concept of Identity is critical to what we do. If it didn't exist, how would it change your approach and how would you answer the question?
The world through a CISO's eyes
The concept of Identity is critical to what we do. If it didn't exist, how would it change your approach and how would you answer the question?
An interview with The Times (UK) around the need for an effective awareness and training program to manage the rapid growth of the remote workforce.
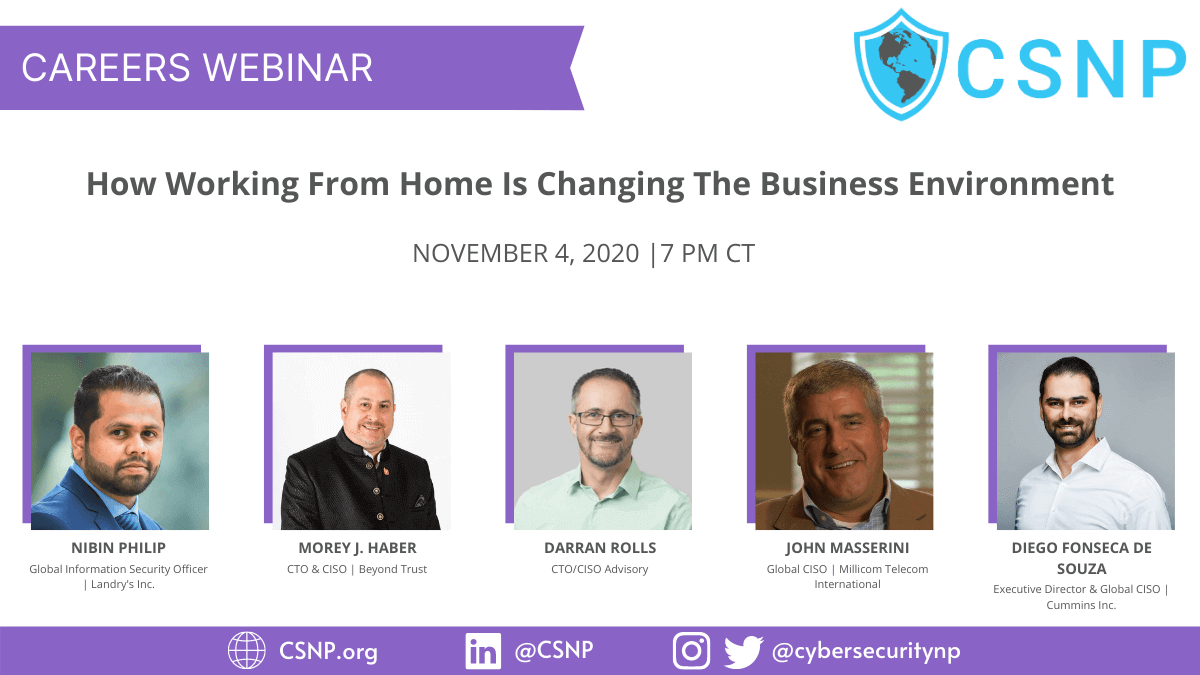
I recently had a wonderful opportunity to sit in on a panel discussing how the pandemic is going to change the way security practitioners think about protecting their organizations.
I had the honor of participating in the LinkedIn Live event on some of the scarest things I have ever heard from my security team.
I had an opportunity to reflect on what is takes to be a CISO, how I got here, and where I think the industry is heading.
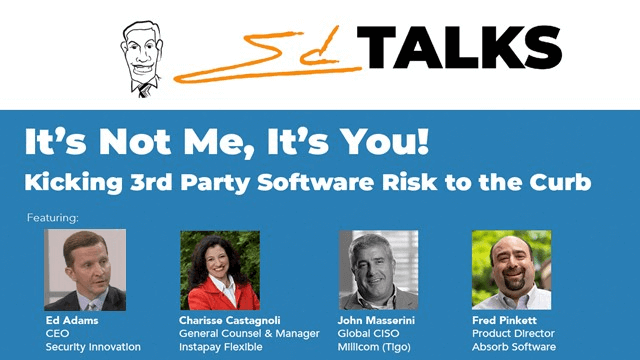
Panel discussion on third-party risk. Topics included conducting software composition analysis (SCA), assessing threats and impacts, risk-rating your inventory, and selecting the right controls.
An interview with the Wall Street Journal around the rapid uptick in enterprise attacks seen amongst the initial weeks of the COVID-19 outbreak.
An interview with the Wall Street Journal around the need for an effective identity management solution to manage the rapid growth of the remote workforce.
In holding myself accountable to my own call-to-action, I have dedicated a page to share all of the diversity-centric resources I have collected over the years. From How-To guides to sites that use lexiconic analysis of job postings to ensure they are bias-free, to awareness training tools, to volunteer organizations.
An interview I did with Ericka Chickowski of DarkReading on the importance of useability of security products.
The outrage over the George Floyd murder is causing many to push for change. Will you use your outrage to fix the diversity issues you see every day?
Chronicles of a CISO was named 2020 Best New Blog of the Year by the Security Blogger Network
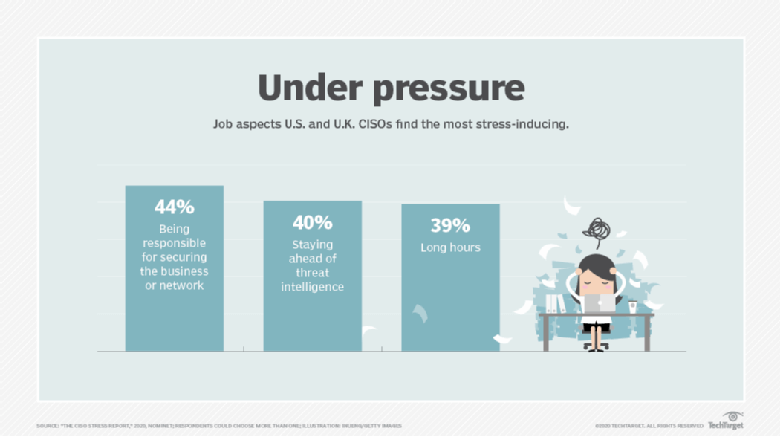
A recent interview I did with SearchSecurity/TechTarget. While much was about the benefits and love of the job, the 'job churn' and 'burnout' discussions are front and center in the industry these days.
This page will list various personal and family-related ‘remote’ STEM activities to participate in as well as other free offerings to help companies, individuals and families cope with their newfound way of working.
With so many people now being asked to work-from-home as part of the evolving COVID-19 precautions, I figured it was worthwhile to put together a few tried-and-true practices to keep you productive and sane while spending an unexpected few weeks in the home office.
A few tried-and-true practices to keep you productive and sane while spending an unexpected few weeks in the home office.
As a hiring manager, how does someone make a person go through three video interviews, do two coding assignments, be so impressed with the coding that they then fly the person up for in-person interviews, and only then decide the coding skills aren’t exactly what they are looking for?!?
It’s hard to believe it’s been a year already. Twelve months ago, I took the leap and decided that it was time to start my own blog, and now, here…
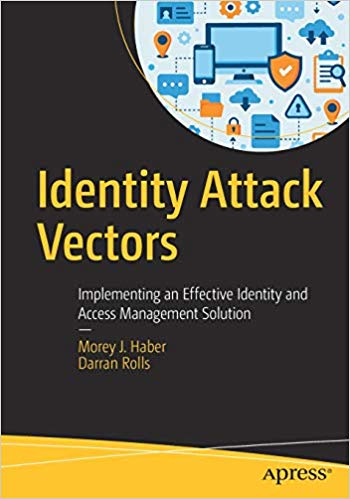
Honored to have had the privilege to write the forward to the third book of Morey Haber‘s trilogy of enterprise attack vectors. This installment, written with Darran Rolls, discusses the…
This is an abbreviated version of my Identity Catechism piece that I wrote in early 2019. This piece focuses on the three key topics to focus on when planning and…
After countless years of presenting to boards, executives, and colleagues, I’ve found that I’ve developed almost a split-personality when I’m asked about what metrics to track.
This is an interview with George Hulme is an internationally recognized writer who has been covering the technology and information security space for more than 20 years, with pieces appearing…
I’ve had just about enough of the fear mongering and lazy ‘reporting’ that’s been in the press recently around how two-factor authentication is broken. I’m not sure about you, but…
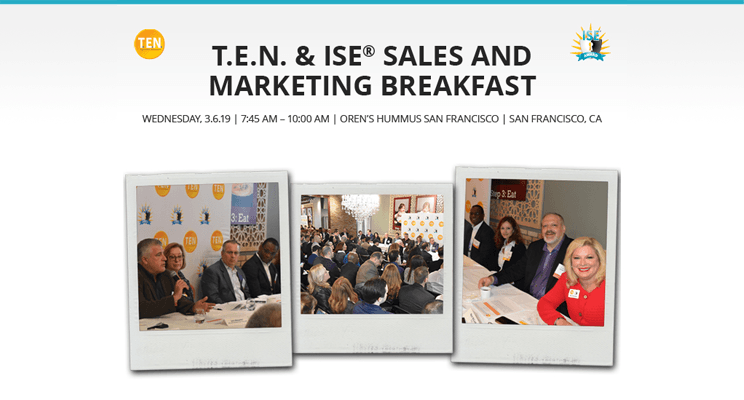
For a number of years, I’ve had the honor of participating on the T.E.N. ISE® Sales and Marketing Breakfast panel at RSA. This year’s panel included some of my most…
A Q&A with John Masserini, CISO at Millicom Telecommunications This Merritt Group blog is part of an ongoing Q&A series with CISOs on preferred marketing and sales techniques, leading up…